Every founder who has tried to wire ChatGPT or Claude into their WordPress site eventually asks the same question in a different wrapper: how far do I let this thing in? The honest answer is that most of the risk isn’t in the AI model itself. It’s in the access you hand it, the credentials you reuse, and the fact that nobody owns the connection once it’s live. This article walks through how to securely connect an AI agent to your WordPress site in Israel the way a senior technical operator would architect it – not the way a tutorial video shows it in five minutes.
Why “just give it the admin login” is the wrong starting point
The fastest way to connect an AI agent to WordPress is to drop your admin username and password into a prompt, a plugin field, or a third-party automation tool. It works immediately. It’s also the single worst decision you can make, because it hands the model (and every service that model talks to) full, unscoped control over your site: content, users, plugins, the database, payment integrations, everything.
The question isn’t whether the AI agent itself is malicious. It’s that admin credentials are now sitting in a third-party system’s logs, in a browser extension’s memory, or in a chat history you don’t control. If that system is ever breached, or if the integration misfires, the blast radius is your entire site – not a controlled slice of it.
How to securely connect an AI agent to your WordPress site
A secure connection is built on scoped access, not shared passwords. In practice this means:
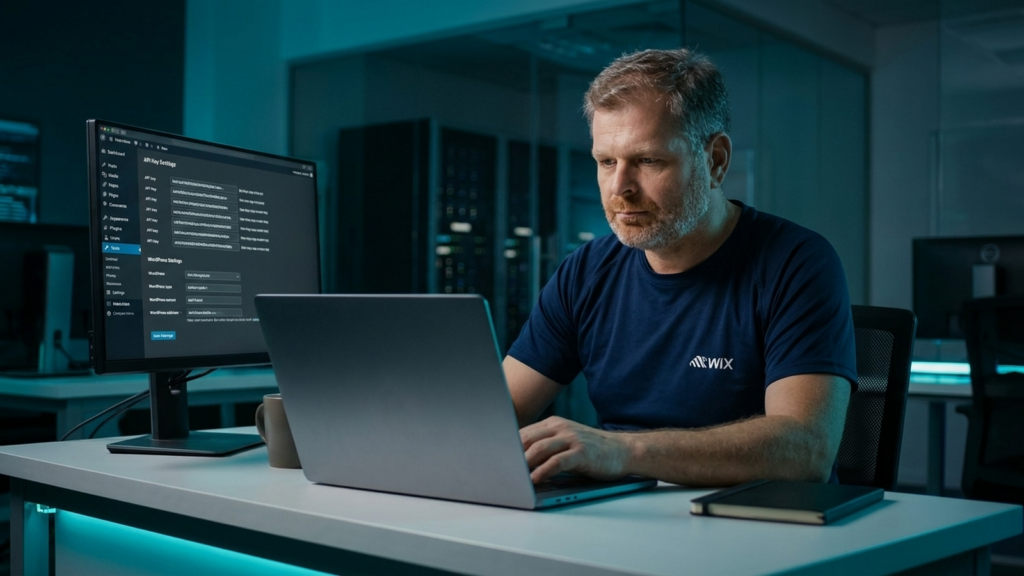
- Use WordPress Application Passwords, not your main login. WordPress has a built-in Application Passwords feature that lets you generate a credential tied to a specific user, specific integration, and nothing else. It can be revoked instantly without touching your real admin password.
- Create a dedicated, limited-role user for the agent. Not an administrator. An editor or custom role that can create and edit posts but can’t install plugins, change users, or touch the database. If the agent only needs to publish drafts, it doesn’t need the keys to the whole house.
- Work through the REST API, not a generic remote-login plugin. The WordPress REST API lets you expose exactly the endpoints you want – posts, media, specific custom fields – and nothing else. Many “connect your AI to WordPress” plugins are far more permissive than they need to be.
- Put the connection behind its own environment, not your main server session. Ideally the agent talks to a staging or API layer that is reviewed before anything publishes to production.
- Log everything the agent does. Every post, every edit, every API call, timestamped and attributable. If something goes wrong, you need to know what the agent touched within minutes, not days.
None of this is exotic. It’s the same least-privilege thinking you’d apply to any third-party vendor – the AI agent just happens to be a very fast, very confident vendor that never asks twice before acting.
Secure ChatGPT WordPress integration in Israel: what actually matters
When businesses in Israel ask about secure ChatGPT WordPress integration, they usually mean one of two things: connecting via a Custom GPT with Actions, or using a no-code automation tool (Zapier, Make, n8n) that bridges ChatGPT and WordPress. Both are fine patterns – if scoped correctly.
For Custom GPT Actions, define the OpenAPI schema narrowly. Don’t expose your full WordPress REST API surface; expose only the three or four endpoints the GPT actually needs (create draft post, update specific meta field, fetch categories). For automation platforms, the same rule applies to the connection you authorize inside the tool – use the scoped application password, not the owner account, and double check what the automation platform itself logs and stores, since that becomes a second place your credentials now live.
One detail founders in Israel often miss: hosting location and data residency. If your WordPress site, customer data, or any regulated information sits under specific compliance requirements, make sure the AI layer and any automation middleware you use don’t quietly route that data through servers or retention policies that conflict with your obligations.
Is it safe to connect Claude to business accounts?
This is really the same question in a different outfit. Claude, like ChatGPT, is a model – it doesn’t “store” your Facebook page or WhatsApp account by itself. The safety question is entirely about the connectors, integrations, and permission scopes you grant it, and about what the underlying platform (Anthropic, Meta, the automation tool in between) retains from that connection.
Before connecting Claude – or any LLM agent – to Facebook, WhatsApp Business, email, or CRM accounts, ask three questions:
- What exact scope of data can this connection read and write – not what the vendor says it does “usually,” but what the API token actually permits?
- Where does the conversation history and connector output get stored, and for how long?
- If this token leaks, what is the worst thing someone could do with it – and is that acceptable?
If you can’t answer all three clearly, the connection isn’t ready for production, regardless of which model is on the other end.
AI agent security for business website: the data boundaries that matter
Think of AI agent security for business website integrations as a set of boundaries, not a single switch:
- Credential boundary: scoped, revocable, never reused across tools.
- Data boundary: the agent only sees the fields it needs – don’t expose customer PII, payment data, or internal notes through an endpoint it doesn’t require.
- Action boundary: read vs. write access defined separately. Many integrations only need to read; don’t default to write access out of convenience.
- Review boundary: a human or a secondary automated check sits between the agent’s output and anything that publishes, sends, or charges.
This is the same model we’d use to wire up any third-party system to a client’s infrastructure – the fact that it’s an LLM agent doesn’t change the discipline, it just raises the stakes because these agents act faster and more autonomously than a typical integration.
Secure LLM integration for SaaS site architectures
For SaaS teams, the stakes are higher because the AI agent often sits near production data and paying customers. A secure LLM integration for SaaS site setup typically separates the agent’s access into its own service account with its own rate limits, its own audit trail, and its own kill switch that a human can flip without touching the rest of the stack. If the agent is summarizing support tickets, it shouldn’t also have write access to billing. If it’s drafting marketing content on WordPress, it shouldn’t be anywhere near your user database.
The mistake we see most often isn’t a dramatic breach – it’s quiet scope creep. An integration set up carefully in month one accumulates extra permissions over month six because someone needed “just one more field” and nobody owned the review.
Who should actually own this connection
This is the part most teams skip: someone has to own the AI integration the same way someone owns your database or your deployment pipeline. Not a freelancer who sets it up once and moves on – a named person who understands your WordPress environment, your data sensitivity, and your compliance posture, and who reviews what the agent is doing on an ongoing basis. That’s the gap Whist’s operator model is built to close: a senior technical owner assigned to your environment, accountable for exactly this kind of integration, rather than a one-off task handed to whoever’s available.
FAQ
What’s the safest way to connect ChatGPT to a WordPress site?
Use WordPress Application Passwords tied to a limited-role user, connect through the REST API with only the endpoints you need exposed, and log every action the agent takes. Avoid sharing your main admin credentials with any plugin or automation tool.
Is it safe to connect Claude to business accounts like Facebook or WhatsApp?
It can be, but safety depends entirely on the scope of the connector and where the data is stored afterward, not on the model itself. Check exactly what the API token permits, where conversation and connector data is retained, and limit access to read-only where possible.
Can an AI agent accidentally publish or change something on my site?
Yes, if it has write access and no review step in between. Build a human or automated check before anything the agent produces goes live, especially for publishing, sending, or billing actions.
Do I need a developer to set this up securely, or can I do it myself?
You can set up a basic scoped connection yourself using Application Passwords and a limited user role. For anything touching customer data, payments, or regulated information, it’s worth having a senior technical person review the architecture before it goes live.
Comments & questions